The checks behind every client you take on.
Selling a business address in Spain makes you an obliged entity under article 2.1.o of Ley 10/2010, Spain's anti-money-laundering law. Flentix runs identity and sanctions checks on every client, before they pay, using a specialist provider independently certified to ISO/IEC 27001, and keeps each client's file, so you can meet your obligations with less work.
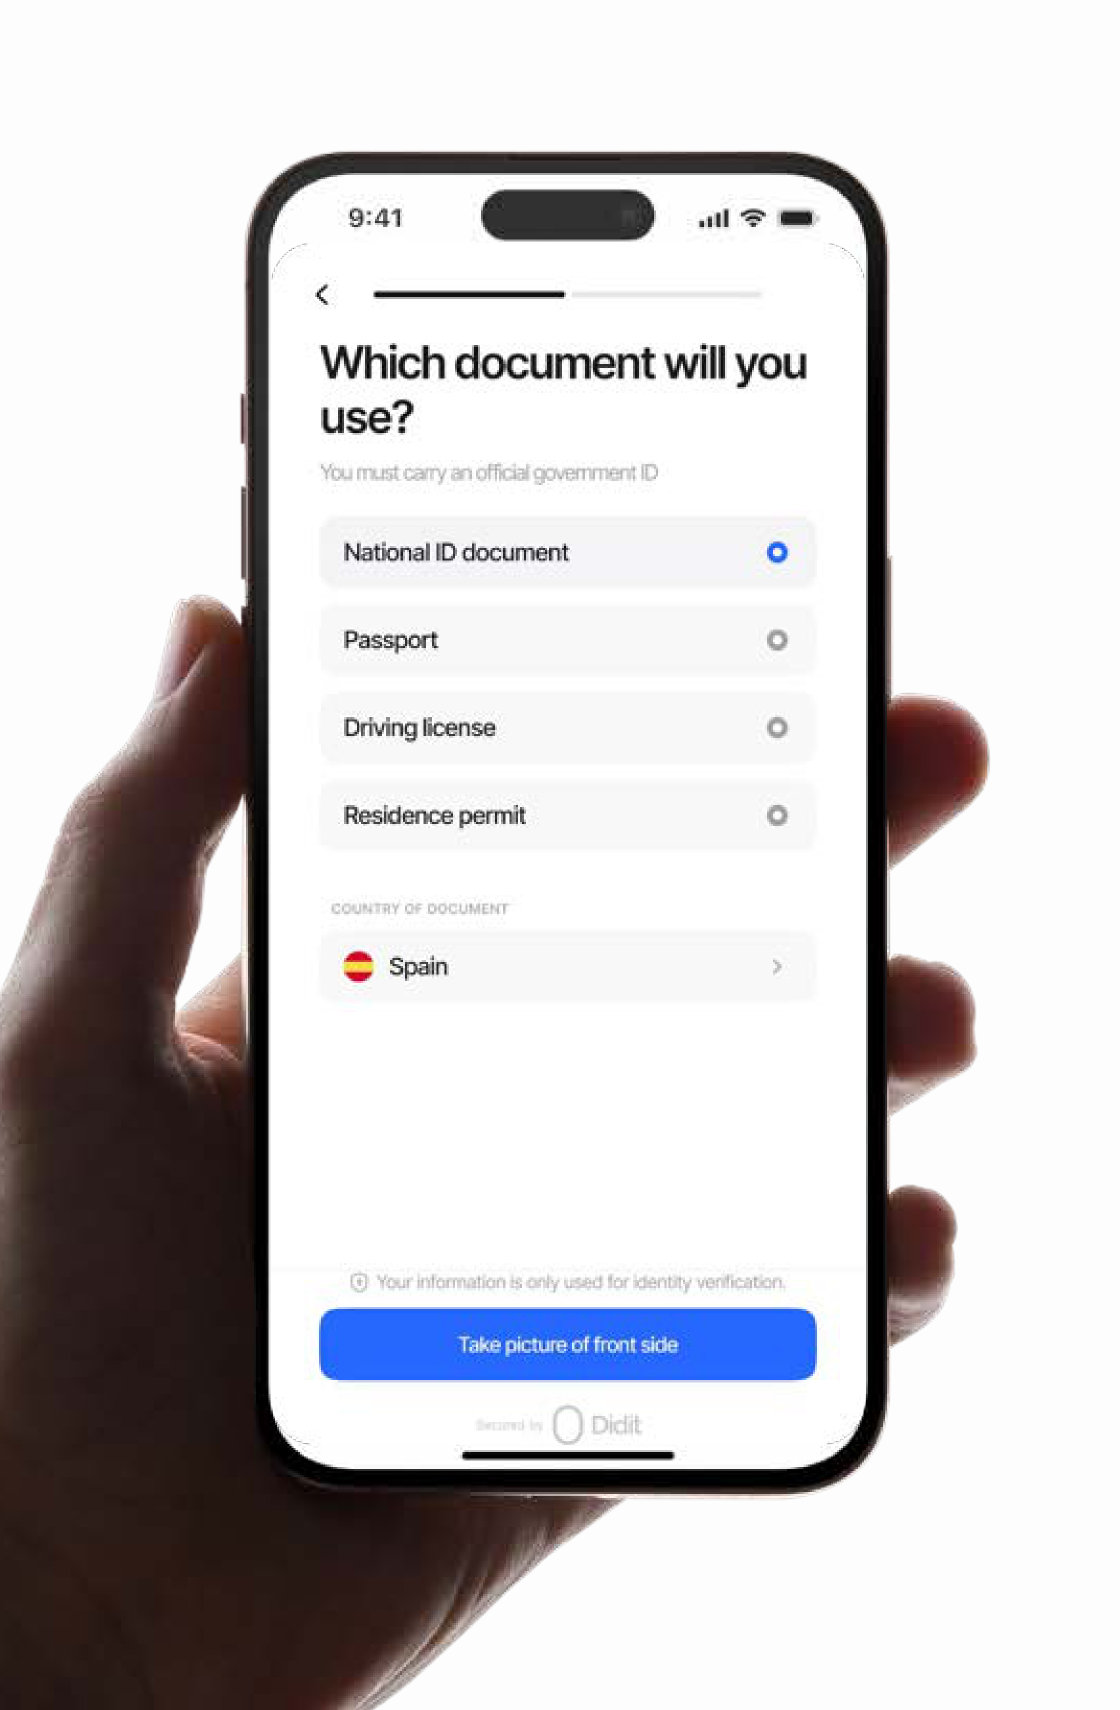
- identity checked before payment
- Every clientidentity checked before payment
- sanctions and politically-exposed-person screening
- Worldwidesanctions and politically-exposed-person screening
- every client re-screened
- Every dayevery client re-screened
- records kept, as the law requires (Ley 10/2010, art. 25)
- 10 yearsrecords kept, as the law requires (Ley 10/2010, art. 25)
Our identity partner
A provider that took its identity technology through Spain's regulatory sandbox.
Every identity check on Flentix is carried out by Didit. We contract with its European company, Didit Identity Spain, S.L., in Barcelona.
Didit's digital-identity project completed testing in Spain's official financial regulatory sandbox, set up under Ley 7/2020, with the CNMV as supervising authority and SEPBLAC, Spain's anti-money-laundering authority, taking part. In those tests, its screening picked up a person wanted by the FBI and a politically exposed person, and its liveness check rejected hyper-realistic masks.
Credentials
Independently certified, tested and audited.
These are Didit's own credentials — the standards the company that checks your clients is held to.
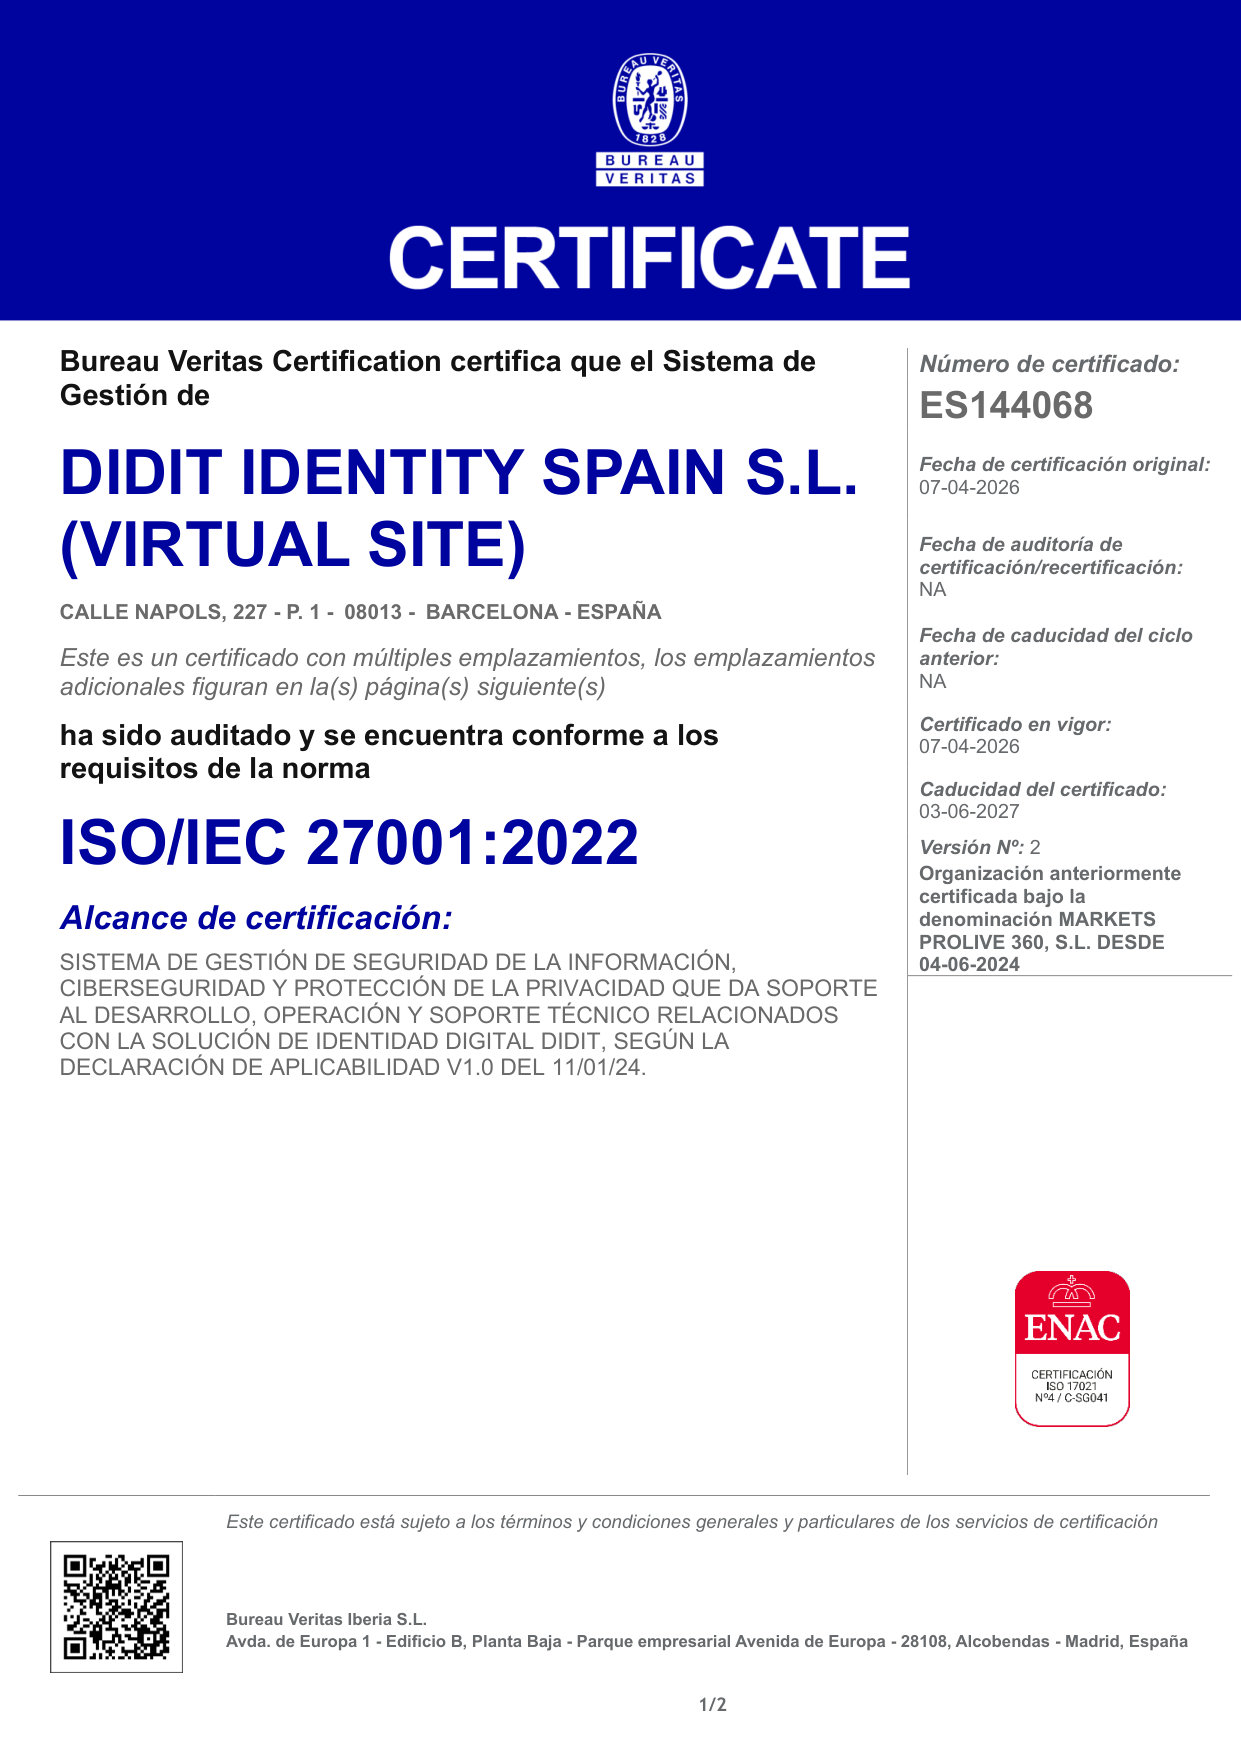
ISO/IEC 27001:2022
Information security certified by Bureau Veritas, accredited by ENAC, Spain's national accreditation body. Certificate ES144068, valid to June 2027.
SOC 2 Type 1 and Type 2
Independent audits in 2026 of Didit's security, availability and confidentiality controls, and of how they operate over time.
Anti-spoofing tested
Didit's biometric authentication product was tested to ISO/IEC 30107-3 at a NIST-accredited laboratory: 360 attempts to fool it with masks, photos and screens, across six attack types. None got through.
Independent legal opinion
An independent legal opinion obtained by Didit concludes that its remote onboarding meets the European Banking Authority's guidelines on remote customer onboarding and is compatible with the EU's new anti-money-laundering rulebook.
14,000+ document types
Official identity documents from more than 220 countries and territories are recognised and checked.
200+ fraud signals on every check
Didit's dedicated fraud team builds the models that look for deepfakes, injected camera feeds, tampered documents and synthetic identities, and updates them as new attacks appear.
The client's check
What happens when someone buys.
It takes the client a couple of minutes on their phone. Nothing to install.
- 01
Their ID
They photograph an official photo ID: a passport, national identity card or residence permit, from any country. Didit checks it is genuine: not a copy, not a screen, not altered.
- 02
A live selfie
They take a short live selfie and follow a simple movement, which checks that a real person is present, not a photo or a recording.
- 03
Face match
The selfie is matched against the photo on the document.
- 04
Screening
The person is screened against sanctions and politically-exposed-person lists worldwide. For a company, its beneficial owners and officers are screened too (Ley 10/2010, arts. 4, 14 and 42).
- 05
Your review
The full result lands in your console, and a trained person on your team reviews and approves it.
- 06
Every day after
Every client is re-screened daily for as long as they are with you (Ley 10/2010, art. 6). A confirmed sanctions match stops their service at once and shows on your screen.
You stay in control
You decide who goes live.
Somebody in your office completes a short online training module, about five minutes with nothing to attend, and signs a declaration (Ley 10/2010, art. 29). The system then lets them approve clients, and the record shows who trained and when. Train as many of your team as you like.
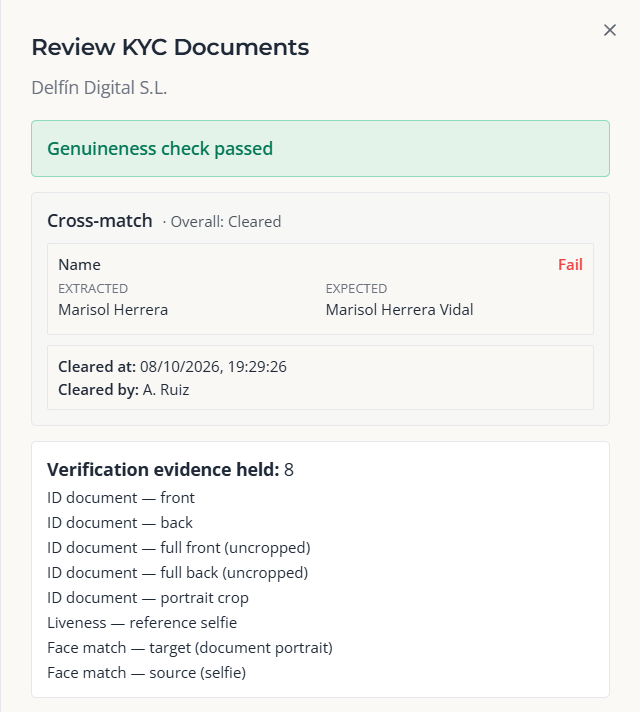
Each client's identity file shows you everything in one place: the document, the selfie, the face-match result, the screening result, and the company's beneficial owners and officers.
Your team reviews every file before the client goes live, without exception. Anything uncertain, like a name that doesn't match, is clearly flagged for whoever reviews it.
Every decision is recorded with who made it and when.
Record-keeping
The record an inspector asks for.
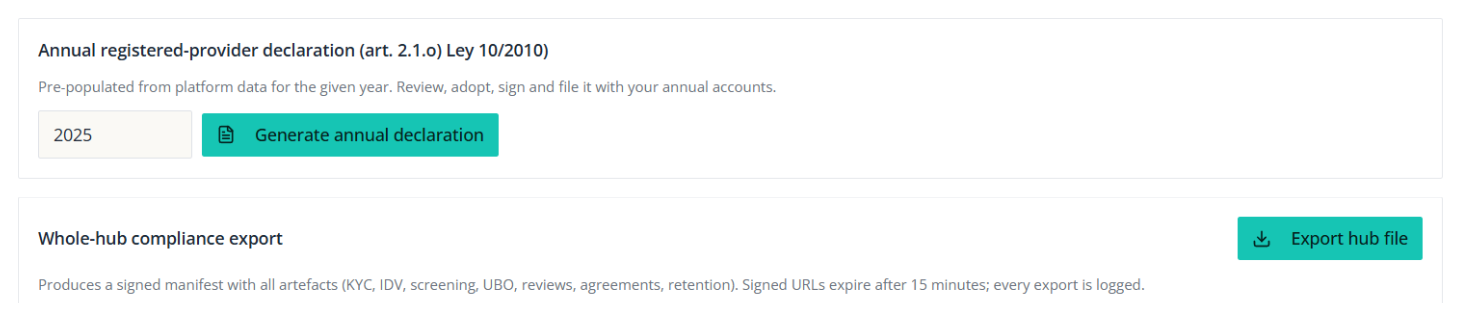
Spanish anti-money-laundering law requires you to keep each client's records for ten years after they leave (Ley 10/2010, art. 25). Flentix keeps them for you.
Kept for ten years
Each client's identity check and screening results, and every decision on that client, stored for the full period the law requires.
Ready in one click
The complete file for any client, exportable whenever an inspector or auditor asks.
VeriFactu-ready invoicing
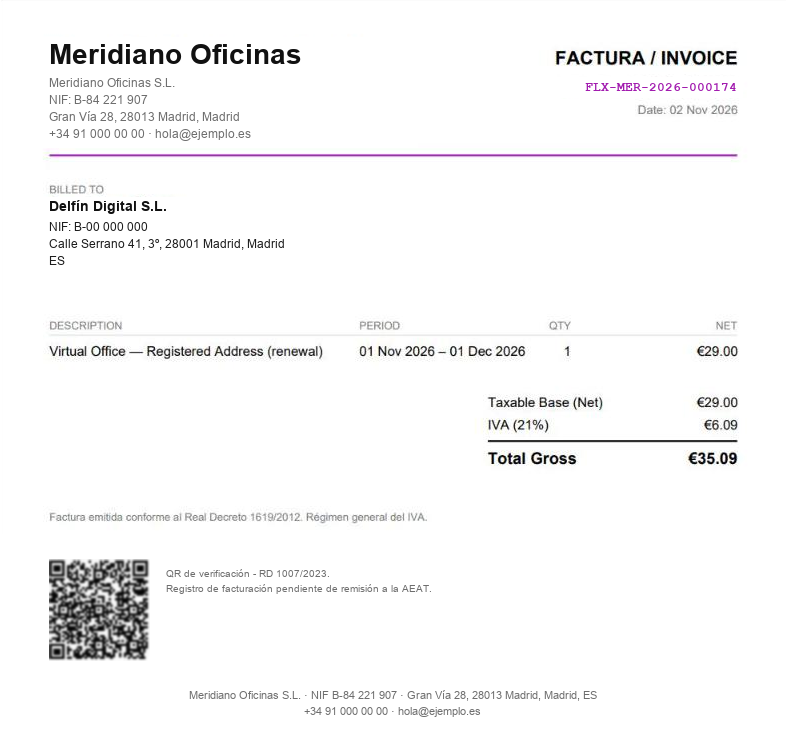
Every invoice you issue through Flentix is in your name, numbered in its own series and built for Spain's VeriFactu rules, with the QR code they call for. Past invoices cannot be altered.
Every agreement kept word for word
Each agreement you accept is stored with its exact text, and a copy is emailed to you.
Payments
Your clients pay you, directly.
Payments for your virtual offices are taken by Stripe, certified to PCI DSS Level 1, the highest level of security in the card industry. The money goes straight into your own Stripe account. Card numbers go straight to Stripe and never pass through Flentix, and our fee is taken automatically by Stripe, so we never hold the money your clients pay you.
Hosting
Your clients' database, hosted in Europe.
Database in the European Union
Flentix's database is in Frankfurt. Didit's primary processing infrastructure is in the European Economic Area.
Walled off
Each business's data is separated from every other business's at the database level.
Copied every night
An encrypted copy of the database is made every night and stored separately from our hosting provider.
Where a supplier works outside the EU, it does so under the safeguards the GDPR provides, and every supplier is named in the agreement you accept.
Showing this to your lawyer or gestor?
We'll send them the detail: how each check works, what is kept and for how long, where the data is held, and the suppliers involved. Ask at support@flentixsystems.com.